6 high tech Army labs to weed out foreign bugs from drones, CCTV cameras
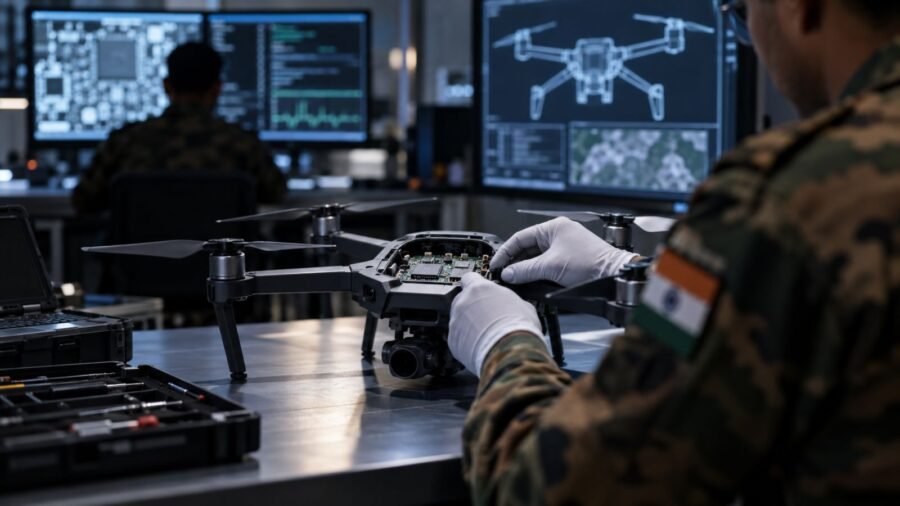
The Indian Army will soon be operating six AASHVAST labs across the country, where all its drones—and eventually CCTV cameras too—will undergo mandatory inspections to identify and eliminate firmware-level vulnerabilities. This will ensure that these do not fail during operations in contested zones and can perform their tasks effectively.
AASHVAST stands for Assessment and Analysis of Electronic Systems Hardware for Vulnerabilities and Security Threats. Currently, one lab has been inaugurated in Delhi, with plans to establish at least five more in the coming months.
AASHVAST, a Firmware Analysis and Validation Suite, developed by QuickPay Pvt Ltd for the Directorate General of Electronics and Mechanical Engineering (DG EME), is designed to do more than just physically inspect drones. It also examines the software that operates these unmanned aerial vehicles (UAVs) – to identify and eliminate firmware-level vulnerabilities.
Story continues below.
Subscribe to see fewer ads.
The Army has published a Request for Proposal in April this year to procure customised licensed software for validation of firmware and embedded systems for electronic components, including UAV components.
On August 14, the Indian Army’s Additional Directorate General of Public Information had posted on X: “Equipped with advanced capabilities AASHVAST will enable evaluation of critical defence platforms thereby increasing cyber resilience. Aligned with the national vision of #AtmanirbharBharat, the facility will strengthen operational readiness as well as promote growth of the domestic defence ecosystem.”
While the lab will initially test all drones, sources said that CCTV cameras procured by the Army in future will also eventually be inspected by it for Chinese proprietary protocols or equivalent, which could be potentially embedded in these.
The idea behind establishing these labs, a first of its kind, was to neutralise the common threats of enemy interference in Indian drones, preventing them from performing their designated tasks in a contested area, Rajib Roy, Director of QuickPay Pvt Ltd, told .
Story continues below this ad
So far, drones procured by the Indian Army did not have firmware-level vulnerabilities checked. The suite will close this critical gap.
Firmware vulnerabilities can be introduced during the manufacturing stage of a component or an upgrade process. For instance, unused codes could be introduced, hidden commands could be invoked at a certain location – thereby preventing the drone from performing its task.
There are approximately 14 types of vulnerabilities that the labs can detect. These include geospatial vulnerabilities, such as a malfunction that occurs when flying over a certain location, or issues that prevent a drone from reaching its preset destination. Other vulnerabilities involve unused and hidden codes that could cause a drone to terminate before reaching its target. Additionally, there are time and location bugs that may cause a drone to operate normally except at specific times or locations.
The use of Chinese components in military drones has been a cause of concern for India, especially since many of these drones are used in operations along the eastern borders. Considering significant national security risks and possible data vulnerabilities, India has previously prohibited domestic military drone manufacturers from using parts made in China. In 2025, the Army Design Bureau submitted a detailed framework to the Ministry of Defence aimed at eliminating Chinese-origin components from UAVs.
Story continues below this ad
People involved with the project said that AASHVAST labs will also examine drones for Chinese and/or other foreign-origin active components, as well as hidden passwords, embedded keys, remote access tools and location-based security controls.
“This will help prevent situations where active components sourced from China are misrepresented as ‘made in India’ or another country, based solely on the invoice indicating their point of purchase,” a person involved with setting up the lab said.
“There is no mechanism to determine what is embedded within the silicon. What is visible is merely the invoice, which shows (from) where the part was purchased. But that does not necessarily indicate its true origin,” the person said.
Broadcast industry calls for immediate restoration of BARC TV ratings
By Sohail Khan · 21 Sep
ED chargesheets EaseMyTrip promoter in Mahadev betting app case, seeks to confiscate shares
By Sohail Khan · 21 Sep
‘Rock Star’ of Kuno is gone: Gaurav, an original Project Cheetah big cat, dies
By Sohail Khan · 21 Sep
Leave a Reply